
AI Governance & Shadow AI Control
Moftgate AI Governance makes all AI usage visible in one pane: installed AI clients, AI website visits, and OAuth-connected AI plugins on corporate accounts. Web Content Gateway and Web DLP enforce your policy and produce audit-ready evidence.
AI Platform Activity & Action Logs
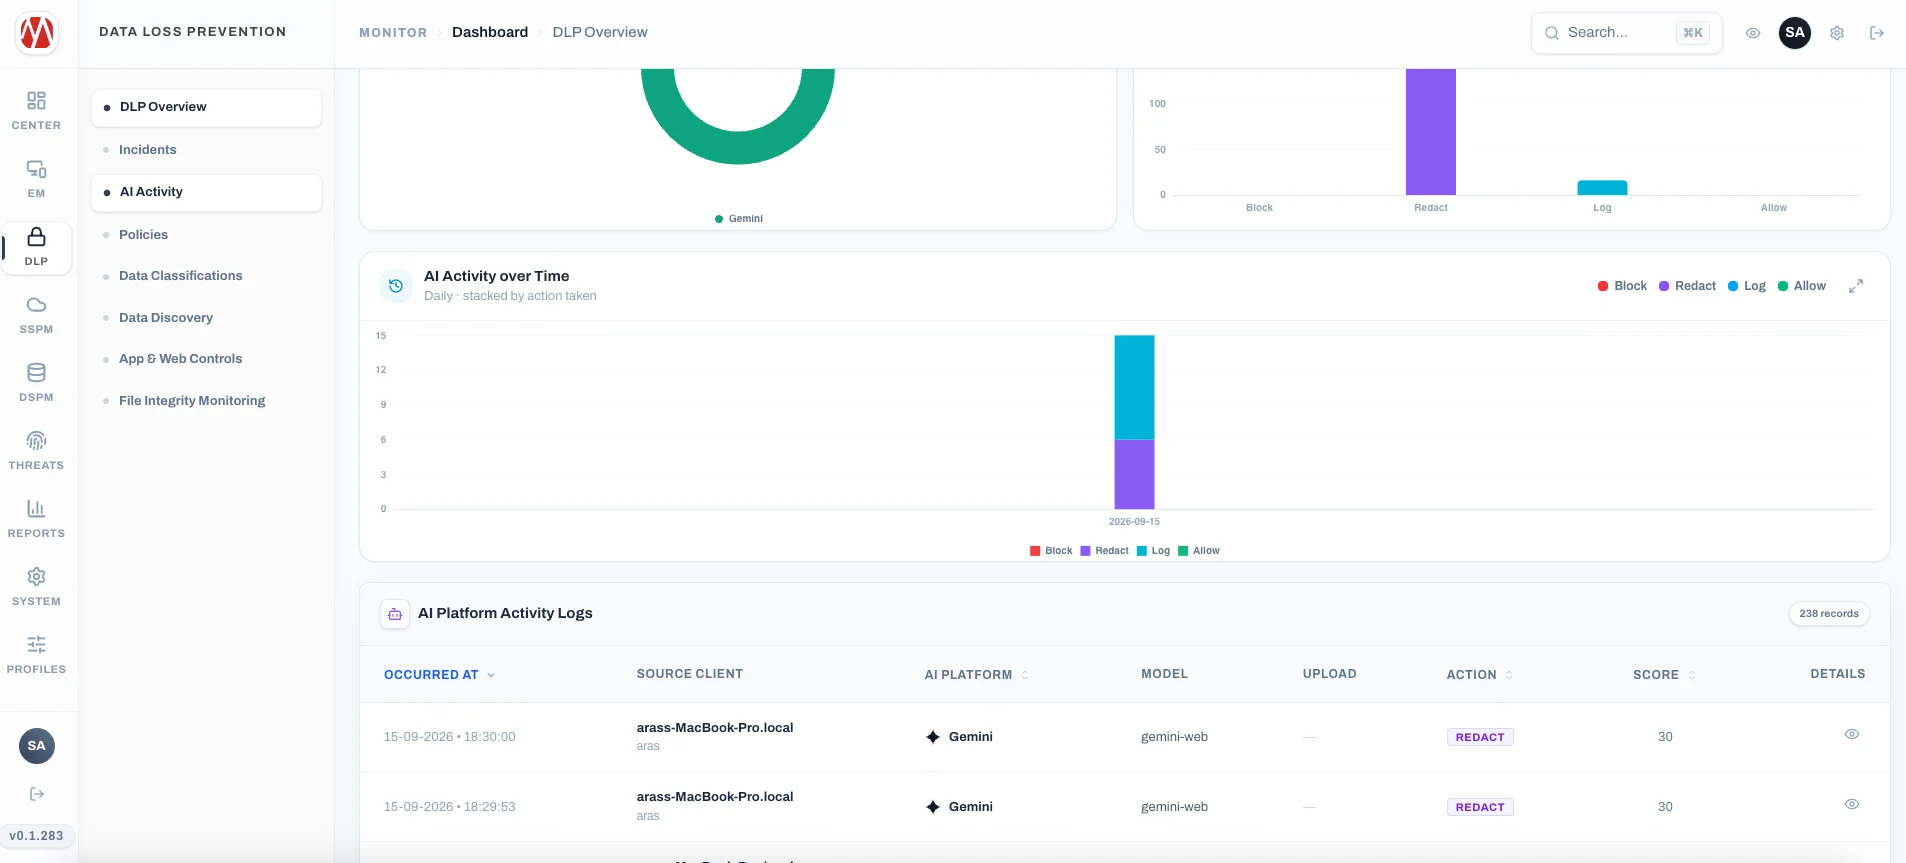
AI usage you cannot see is a data leak you cannot control
Legacy management tools cause operational friction, performance degradation, and critical security blind spots.
- ✕Employees pasting customer lists or source code into public AI tools goes unnoticed.
- ✕No one knows who uses which AI service or how often; written policy cannot be enforced.
- ✕AI plugins authorized with corporate email can gain access to mail, drive, and calendar content.
- ✕Audits ask "how do you enforce your AI usage policy?" and there is no evidence to present.
What Does AI Governance & Shadow AI Control Deliver?
All capabilities operate through a single lightweight agent and central web console; no additional servers or hardware required.
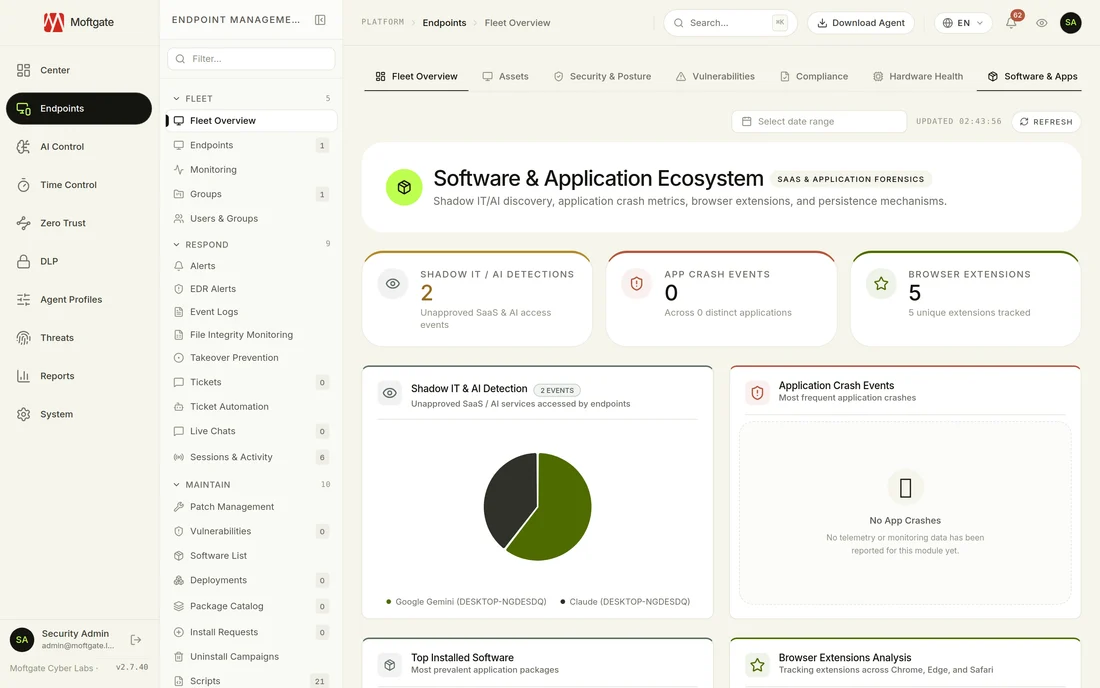
Shadow AI discovery
Automatically inventories which AI tools are used by whom across endpoint, web, and SaaS layers: installed clients, site visits, and OAuth-connected plugins.
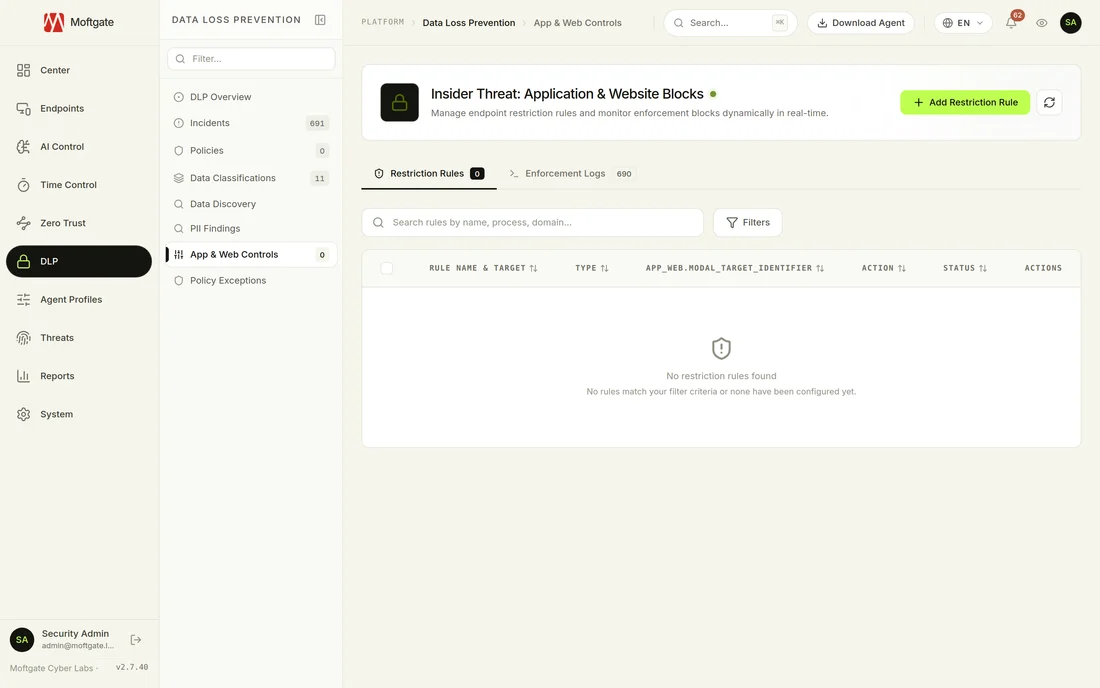
AI site blocking & coaching
Web Content Gateway blocks unapproved AI sites or shows an in-page coaching warning; approved services keep working uninterrupted.
Corporate tenant restriction
Restricts sign-in to approved AI services to corporate accounts only; personal-account sessions are blocked.
AI prompt DLP protection
Web DLP catches sensitive data pasted into AI chat boxes or uploaded to AI sites on the endpoint, before encryption.
Group-based AI policies
Different rules per department: approved coding assistants for developers, a stricter list for finance.
Audit-ready evidence
Every block and warning is recorded with user, device, and timestamp, and feeds GDPR / ISO 27001 reports automatically.
Deploy in Four Steps
- 1
Discover usage
The agent inventories installed AI clients, AI site visits, and OAuth-connected AI plugins automatically.
- 2
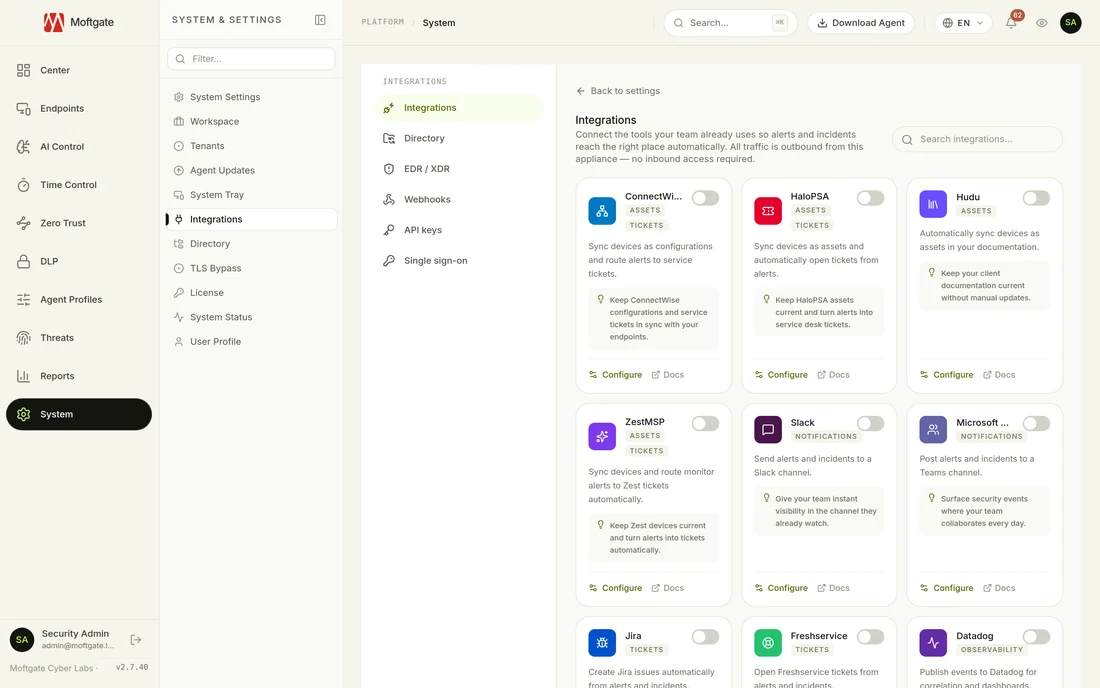
Write your allow list
Define which AI services are allowed and which are banned in your policy.
- 3
Turn on enforcement
Rules reach all devices at the next heartbeat; block, warn, or allow takes effect instantly.
- 4
Report the evidence
AI usage trends and blocked attempts are fed into audit reports automatically.
Full Compliance with Global Standards
Protect corporate continuity, pass regulatory audits, and ensure sovereign data governance.
- ✓See which AI tool runs on which device within minutes
- ✓Reduce unapproved AI usage with coaching warnings
- ✓Stop data leaks into AI prompts at the source
- ✓Present AI usage evidence to auditors in one click
- ✓Lock approved AI tools to corporate accounts
Everything You Need to Know
Explore Integrated Security Modules
Centralized Endpoint Management
Manage all Windows, macOS, and Linux endpoints from a single unified console. Deploy software silently, automate security patches, and provide live remote support without interrupting employees.
Data Loss Prevention (DLP)
Protect customer data, financial records, and trade secrets from leaving company computers. Block unauthorized USB transfers, cloud uploads, and clipboard leaks in real time.
Employee Productivity (Time Control)
Measure application and website usage on the endpoint, classify it as productive, neutral or unproductive with your own rules, and see the productivity score per person, team and day.
Zero Trust Network Access (ZTNA)
Identity-verified, posture-checked, least-privilege secure access: protect access to private applications with granular microsegmentation.
Learn More About This Topic
Deploy AI Governance & Shadow AI Control in Your Organization
Test all module capabilities on your private infrastructure with a 14-day enterprise trial.